
[ad_1]
User Enrollment is designed for BYOD—or bring-your-own-device deployments—where the user, not the organization, owns the device.
User Enrollment and Managed Apple IDs
User Enrollment requires Managed Apple IDs† These are owned and managed by an organization and provide employees access to certain Apple services. In addition, Managed Apple IDs†
-
Are created manually, or automatically using federated authentication
-
Are integrated with a Student Information System (SIS) or uploading .csv files (Apple School Manager only)
-
Can also be used to sign in with an assigned role in Apple School Manager or Apple Business Manager
When a user removes an enrollment profile, all configuration profiles, their settings, and managed apps based on that enrollment profile are removed with it.
User Enrollment is integrated with Managed Apple IDs to establish a user identity on the device. The user must successfully authenticate for enrollment to be completed. the Managed Apple ID can be used alongside the personal Apple ID that the user has already signed in with; the two don’t interact with each other. User Enrollment is designed for devices owned by the user.
User Enrollment and federated authentication
User Enrollment works with Microsoft Azure Active Directory (AD) or Google Workspace and Apple School Manager or Apple Business Manager and a third-party MDM solution. For your users to take advantage of synchronization with Azure AD or Google Workspace and User Enrollment, your organization must first:
-
Configure Azure AD or Google Workspace
If you have a local version of Active Directory, additional configuration must be taken to prepare for federated authentication.
-
Sign up your organization in Apple School Manager or Apple Business Manager
-
Set up federated authentication in Apple School Manager or Apple Business Manager
-
Configure an MDM solution and link it to Apple School Manager or Apple Business Manager
-
(Optional) Create Managed Apple IDs
User Enrollment and managed apps (macOS)
User Enrollment has added managed apps to macOS (this feature was already possible with Device Enrollment and Automated Device Enrollment). Managed apps that use CloudKit use the Managed Apple ID associated with the MDM enrollment. MDM administrators must add the InstallAsManaged key to the InstallApplication command. Like iOS and iPadOS apps, these apps can be automatically removed when a user unenrolls from MDM.
How users enroll their personal devices
There are two main ways users can enroll a personal device in User Enrollment—through an account or through an enrollment profile.
Account-based user enrollment
In iOS 15 or later and iPad OS 15 or later, organizations can use a streamlined User Enrollment process, built right into the Settings app to make it easier for users to enroll their personal devices.
To do this, the user navigates to General > VPN & Device Management section in Settings, and taps the “Sign in to Work or School Account” button.
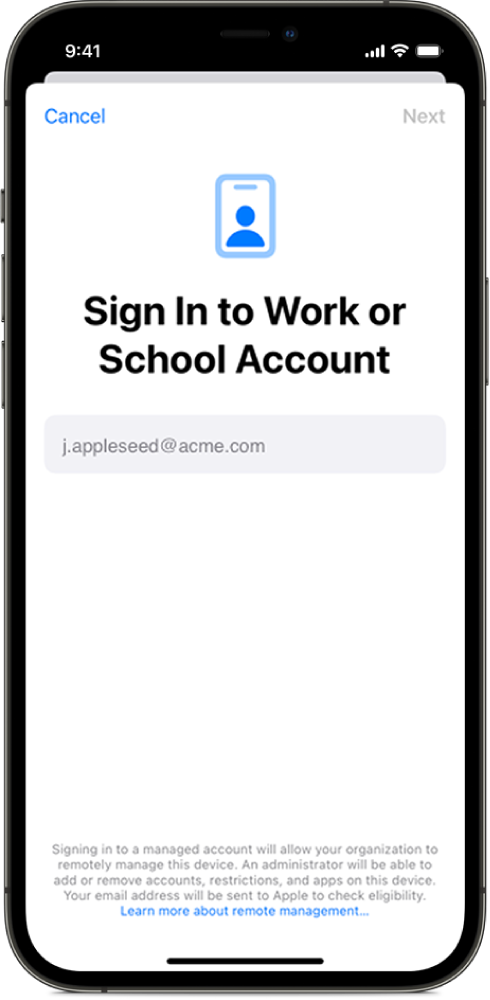
As they enter their Managed Apple IDservice discovery identifies the MDM solution’s enrollment URL.
The user enters their organization user name and password. After the organization’s authentication succeeds, the enrollment profile is sent to the device. Additionally, a session token is issued to the device to allow ongoing authorization.
Finally, after a user is signed in, the new managed account is displayed prominently within the Settings app.
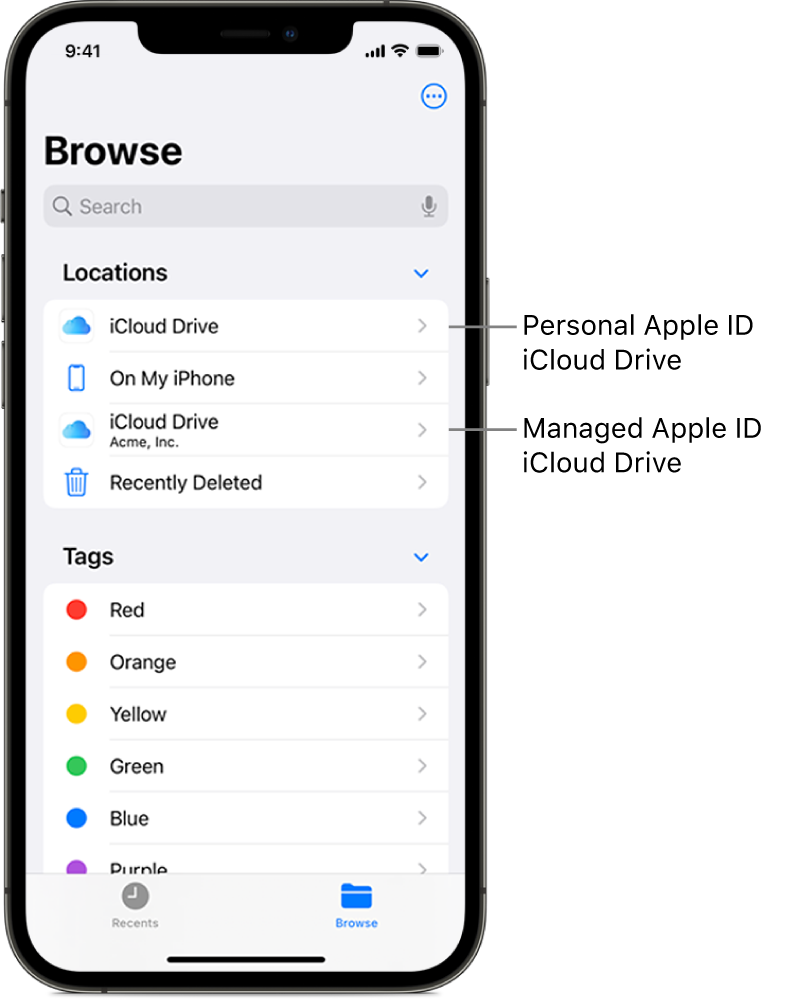
After enrollment, users can still access files in their personal iCloud Drive† the iCloud Drive for the organization appears separately in the Files app. In iOS and iPadOS, managed apps and managed web-based documents all have access to the organization’s iCloud Drive—and through existing restrictions, the MDM administrator can help keep specific personal and organizational documents separate.
Users can see details about what is being managed on their personal device and how much iCloud storage space is provided by their organization.
Profile-based User Enrollment
With the existing profile-based User Enrollment flow, users are provided an enrollment profile using a customized URL, mail message, or by other means. After the enrollment profile and any additional configuration profiles are downloaded, a User Enrollment screen appears and the user clicks Enroll My (iPhone, iPad, iPod touchMac), then:
-
With federated authentication: Enters their Microsoft Azure AD or Google Workspace email address and password
-
Without federated authentication: Enters their Managed Apple ID username and password
When enrollment is complete, users see an additional account in Settings > Passwords & Accounts on iPhone, iPad, and iPod touch devices and in System Preferences on Mac.
Because the user owns the device, User Enrollment has a limited set of payloads and restrictions that can be applied to the device. For the complete lists, see User Enrollment MDM information.
How Apple separates user data from organization data
When User Enrollment is complete on an iPhone, iPad, or iPod toucha separate volume is automatically created on the device and contains managed:
In iOS and iPadOS, managed apps and managed web-based documents all have access to the organization’s iCloud Drive through existing Managed Open In restrictions. The MDM administrator can help keep specific personal and organizational documents separate.
System administrators can manage only an organization’s accounts, settings, and information provisioned with MDM, never a user’s personal account. In fact, the same features that keep data secure in organization-managed apps also protect a user’s personal content from entering the corporate data stream.
|
MDM can |
MDM can’t |
|---|---|
|
Configure accounts |
See personal information, usage data or logs |
|
Configure Per-app VPN |
Access inventory of personal apps |
|
Install and configure apps |
Take over management of a personal app |
|
Require a pass code |
Require a complex passcode |
|
Enforce certain restrictions |
Access device location |
|
Access inventory or managed apps |
Access unique device identifiers |
|
Remove managed data only |
Remove any personal data |
|
Remotely wipe the entire device |
|
|
Manage Activation Lock |
|
|
Access roaming status |
|
|
Enable Lost Mode |
Note: Administrators can require passcodes with a minimum of 6 characters and prevent users from using simple passcodes (for example,123456 or abcdef), but can’t require complex characters or passwords.
|
Sources 2/ https://support.apple.com/guide/deployment/user-enrollment-and-mdm-dep23db2037d/web The mention sources can contact us to remove/changing this article |
[ad_2]